We connect what is already there.
One device next to your controllers reads them and passes writes back. Your services use one API for every building.
[03] Use it
One API for every building.
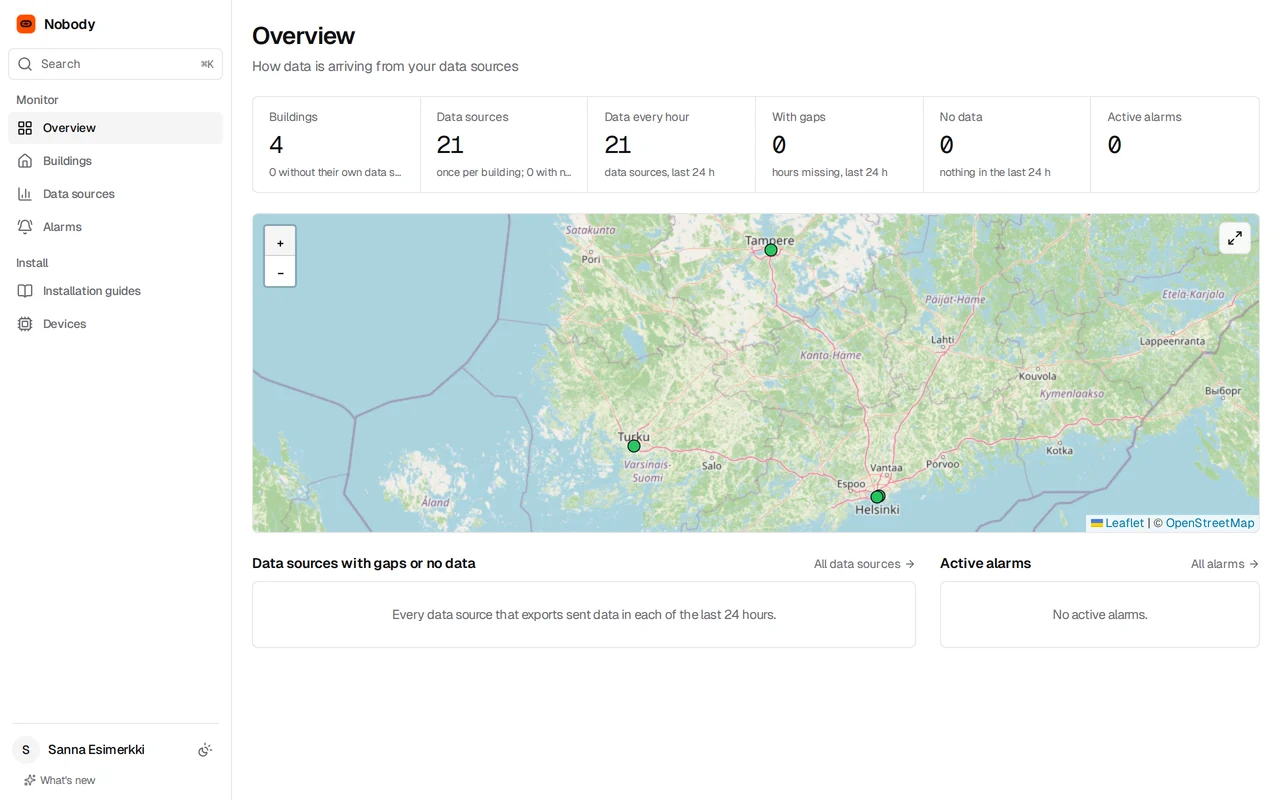
Every point gets the same structure, whatever the system. Read it over REST or MQTT, look at it in the portal, or ask an AI about it.
The details
What is the device?
A small box that goes into the automation cabinet, next to your existing controllers. It connects over its own 4G, so it needs nothing from your network.
What does installation involve?
We work out the setup from photos and ship a configured unit. Your technician mounts and connects it. We commission it remotely, and data usually flows within hours.
What happens if a service stops writing?
Services can change values through the API. Every write carries a fallback: if the service stops refreshing it, the edge unit puts the building’s own value back. Unplug the unit and the building runs as before.
Are writes logged?
Yes. Writes go to the mapped point name, not the controller address, and each one is logged with the value, the service and the time.
How often are points read?
About every minute for the points your services use, hourly for the rest, and a daily scan so new points show up.
Where does it run, and is it secure?
In our cloud in the EU/EEA, Finland-only, or the whole stack on your own servers. Edge units connect outbound only, over TLS, with no open ports on your network. ISO 27001 certification is in progress.
Can people reach the controllers remotely?
Yes. Time-limited portal sessions to a controller’s own web interface, or an on-demand VPN for an authorised system. No open ports either way.
Which outputs are there?
A REST API, MQTT (our broker or yours), a virtual BACnet device, or a push to your endpoint.
Is there a version without an edge unit?
With VPN access, field agents can run in our cloud or yours. That is read-only; writes need an edge unit.